与「Secret」相关的搜索结果
Secret 贴吧
一个关键词就是一个贴吧,路径全站唯一。
用户
未找到
包含 Secret 的内容

🚨BREAKING: Claude is officially a NATIONAL SECURITY THREAT and is BLACKLISTED from the ENTIRE defense supply chain
>anthropic: no autonomous weapons, no mass surveillance, no exceptions
>pentagon blacklists claude as an active national security threat
>anthropic sues
Federal court ruled 2–1 AGAINST Anthropic:
"As Anthropic admits, the company encodes restrictions into Claude that prevent the model from performing tasks that Anthropic wishes to prevent."
"On more than one occasion, these restrictions have stopped Claude from performing tasks requested by government users":
>refused to perform "tasks that were appropriate in a national security context"
>refused CDC queries on infectious disease prevention research
>anthropic questioned claude's use in the military operations
"Anthropic's Chief Science Officer explained how the company 'seek[s] to embed safety considerations directly into the model itself.'"
"[Anthropic's] CEO explained how such training gives the model an 'identity, character, values, and personality' of its own, tethered to a 'constitution' developed to impose 'high-level principles and values' on Claude itself."
"We have no reason to doubt that Anthropic manipulates Claude's function with noble intentions... BUT the statutory definition of a 'supply chain risk' turns on what Anthropic does, not why Anthropic does it."
"In our Republic, it is the President and the Secretary of War who must determine how best to balance the competing risks. In doing so here, the Secretary DID NOT transgress any limits on his authority."
ITS OVER.
ANTHROPIC IPO IN SHAMBLES
显示更多



Google 开源了 "Agent 工作负载的 Kubernetes"「AX」
AX 是为 Agent 设计的声明式编排运行时,你用 YAML 声明一个 Agent 任务,AX 负责在集群中沙箱化、配置环境、管控网络并大规模运行它。
开源地址:
它解决什么问题
项目的立论很清晰:Agent 是一种既有的编排体系都不匹配的新型工作负载。
· 它不像微服务(无状态、常驻),Agent 会持续积累状态(对话记忆、工作区文件、工具会话);
· 它不像批处理作业(跑完即弃),Agent 大部分时间在等待,等模型响应、等工具返回、等人类审批,期间沙箱空转烧钱;
· 它运行的是不可信代码,需要严格隔离;它还调用外部模型 API 和 MCP 工具服务器,需要网络与凭据管控。
架构:四个二进制 + Redis
四个二进制分工:ax(开发者 CLI)、ax-server(无状态 gRPC API)、ax-controller(调和循环)、ax-task-runner(每个任务容器内的 PID 1)。
核心原语:Task / Workspace / Model (+ Gateway)
Task 是最小执行单元:带 CPU/内存限制的隔离沙箱。AX 刻意把它做得细粒度、可自由组合:一个任务可以是全部工作,也可以是任务树的根节点。生命周期用 status.phase + Conditions 表达,支持挂起(检查点保存状态)与恢复。
Workspace 是最有产品想象力的一层。它把“环境准备”声明化:列出需要的 Git 仓库、MCP 服务器、技能包,runner 在命令启动前物化好。更激进的是 generative workspace:你可以只写一句自然语言目标("搭一个 Python 3 开发环境"),首次启动时 runner 会派一个引导 Agent(Antigravity,需 GEMINI_API_KEY,默认限时 10 分钟)去实际安装工具链并验证依赖。声明一次,任意任务复用。
Model 把“用哪个模型、什么参数、密钥在哪”抽成命名资源,密钥引用 K8s Secret。轮换密钥、锁版本、调温度只需一次 ax apply。
沙箱与运行时细节
每个任务容器以 ax-task-runner 为 PID 1:启动元数据服务(端口 80,HTTP/1.1+h2c,暴露 /healthz、/readyz 和任务/工作区自省端点——Agent 不需要 SDK 就能读到自己的配置)、按绑定顺序初始化工作区、然后 fork 出 spec.command 并持续监管。命令退出后 runner 仍驻留,所以 ax ssh 和元数据服务在命令结束后依然可用。停机采用 SIGTERM + 10 秒宽限 + 强杀的两级策略。
安全模型有几处值得注意的门控:guest 服务(任意进程执行与文件读写,ax ssh 的底层)默认关闭,只在 debug: true 时开启——ax ssh 连不上未开启的任务是刻意的安全设计,不是故障;Gateway 用显式 allowlist 管控出站流量,并可向入站请求注入凭据,避免把 API key 直接塞进 Agent 环境。
路线图透露的方向
五大方向:Actor 架构深化、空闲检测自动挂起、有状态任务 fork、任务级 SPIFFE 身份做零信任 mTLS、runner 层自动采集 OpenTelemetry 遥测与结构化 Agent 轨迹。
显示更多


Periodic reminder that Xi is just a wifeguy. He's still very happy he could score with Peng Liyuan, a very famous Chinese idol. Over the entirety of his career prior to becoming the General Secretary, he was mainly known as "that dude who's Peng Liyuan's husband".
显示更多


🦔Someone is buying Japanese used books by the ton. Not novels or comics. Philosophy, history, medical law, Edo-period cultural texts. Multiple buyer accounts all ship to one logistics center in Okayama Prefecture that won't answer questions. Export records show over 50 tons, roughly 100,000 volumes, shipped to the US since last year. No buyer has been identified.
Separately, court documents confirmed Anthropic's "Project Panama" bought millions of books in the US, cut the spines off, scanned them, and shredded the originals. An internal memo said the goal was to "destructively scan all the books in the world." Similar operations have been reported across Europe.
My Take
Anthropic's US book operation came out in court filings earlier this year. Project Panama. Millions of books, cut the spines off, scanned, shredded. Their VP chose the codename so nobody outside the company would find out. That story broke and apparently the same operation just moved to Japan. Anonymous buyer accounts, a warehouse in Okayama that won't take questions, and 100,000 volumes of specialized academic texts that nobody buys to resell.
I don't know how you build a trillion-dollar industry on material you had to acquire in secret through middlemen because you knew the public would object. Authors spent years on those books and now they're fed through a scanner and thrown away so a chatbot can sound smarter. If the data was free to use, they wouldn't need codenames and anonymous warehouses. The lawsuits over who owns this material have barely begun and I think the copyright exposure across the whole AI industry is enormous. Anthropic's internal memo said the goal was every book in the world, which describes the foundation of the product.
Hedgie🤗
显示更多


🟥 What you’re watching is total chaos on the White House lawn. Chinese state media stepped right in taking over front-row spots reserved specifically for the American press pool, triggering a wild shouting match with Secret Service and US reporters.
The real kicker? The same legacy outlets that claimed they’d refuse to give Trump coverage suddenly want a piece of the Trump! 🍿🎥
显示更多


I’ve seen a couple of posts about this so wanted to demystify. Today, every Muse user gets a free computer in the cloud. It's a real computer, and we’ve designed the security architecture of the Muse Secure VM carefully so you and your Muse can do almost anything you could with a computer sitting under your desk while keeping you and the system safe from threats like prompt injection. We wrote about this at length in our security blog post – Activity in the “runtime cell”, which you share with your Muse is unfettered, but sensitive actions are all overseen by the Sentinel, which runs outside of that cell. Similarly, all sensitive secrets - like the passwords you enter into Muse’s secure credential storage - are also stored outside the runtime cell.
The runtime cell gets its own root filesystem (including a full Ubuntu linux image) separate from the host filesystem where your other more sensitive data lives. Because it is isolated from the sensitive stuff that runs on the same box, this means that we can, and do, offer users full visibility and control over the files in the runtime cell. Just as you can when you install Linux on your home computer, you can poke around and see all the files that make the system work - both debian system files and the binaries and data files that implement the parts of Muse which run in the runtime cell.
This was a very deliberate choice - your Muse Secure VM truly is your own computer in the cloud. You can install software in it, write and compile code, use the browser to surf the web: it is your own Linux box that you can operate as you choose with your Muse. Poking around in this computer doesn't give you any privileged access to Meta infrastructure, or to other people's data
If I may geek out a little here for a second… As a kid I loved to take things apart to see how they worked. As a teenager I got into computers and soon found myself drawn to C:\WINDOWS\SYSTEM and the system registry, later Slackware’s /dev/, /proc/ etc – I could see how the system was laid out and as I explored what DLL files and .so files actually did, I gradually became able to meld the computer to my own will.
We’re really proud to be able to put a real computer in millions of people’s hands with a similar level of transparency. We built a file explorer right into the Library tab of the UI. We want you to be able to see the markdown files Muse writes while it thinks about how to serve you better, and explore the internals of the system if you’d like to.
So, when you ask your Muse to show you its entire filesystem, and receive gigabytes of files you’re seeing the full contents of the runtime cell. It’s yours to explore and enjoy!
If you’re not a geek like me, or simply want to download the data that you personally have created directly with your Muse, we added a feature for that too in Settings > Data controls > Download your agent data.
显示更多


THIS IS CRAZY…
Chinese reporters got into a brief CONFRONTATION with US Secret Service and other American reporters!!!


🚨 SlowMist TI Alert 🚨
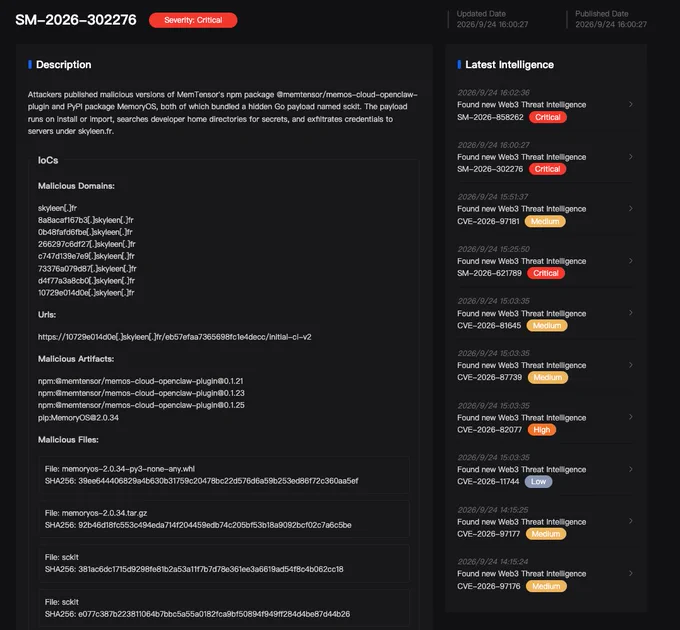
MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's open-source long-term memory library for LLM and AI agents, and memtensor/memos-cloud-openclaw-plugin (npm), the official plugin connecting it to the OpenClaw agent runtime.
Affected versions bundle cross-platform Go binaries that execute when the package is loaded or imported: MemoryOS==2.0.34 on PyPI, and plugin versions 0.1.21, 0.1.23 and 0.1.25 on npm. You are affected if the PyPI version has been imported in your environment, or if the npm plugin is installed and the OpenClaw gateway has been started.
Potential attacker actions include harvesting npm/PyPI tokens, GitHub/GitLab credentials, AWS keys, SSH keys, API tokens, environment secrets, and other developer credentials, with data sent to infrastructure under skyleen[.]fr. The affected npm plugin may also expose user prompt content.
Users should remove or downgrade affected packages to known-good versions (0.1.20 for npm and 2.0.33 for PyPI), terminate sckit processes, block associated infrastructure, review network activity, and rotate credentials accessible from affected environments.
You can also visit to check for free whether the npm packages, pip packages, domains, or IPs you use are safe.
Reference:
As always, stay vigilant!
显示更多

GODDESS OF VICTORY: NIKKE
勝利の女神:NIKKE
D : KILLER WIFE
~ Secret police ~
🚔🚨🚓🚨🚓🚔🚨
@Gyani_cos


SECRETARY RUBIO: Iran can never have a nuclear weapon.
