与「EVM」相关的搜索结果
EVM 贴吧
一个关键词就是一个贴吧,路径全站唯一。
用户
未找到
包含 EVM 的内容

Getting on-chain data shouldn’t be hard—or expensive—for agents. 🤖
xAPI × BlockPI: RPC access to 60 EVM networks, now on xAPI.
🔑 One key.
💸 $3 per million RPC calls.
⚡ Pay As You Go. No subscriptions.
Build on-chain 👉
显示更多


第一用 @midasmarketsxyz 这个交易所让我感到很新奇,给我的感觉:既不是传统 CEX,也不是自己连钱包的那种纯 DEX。
Grok给我的解释是:“带嵌入式钱包的交易前端”
他的优势是可以同时做多链现货 + Hyperliquid 永续
用邮箱 电话 X登录,自动建 Solana + EVM 地址,不给助记词但是可以自己导出私钥(很dex但又不完全dex)
同时三个大板块设计的也很超前
midas同时融合了“首发观点” “新闻” “市场”及一体
1⃣首发观点
可以看到来自很多交易员过去 24 小时的交易信号和想法
有股票/加密货币/meme三个小板块交易员的观点可以借鉴,也有一键跟单交易,非常方便
2⃣新闻
在midas的主页即可查看关于股票/加密货币的今日热点及新闻,甚至还有很多用户的一些快讯和观点供大家参考
3⃣市场
此板块可以交易美股和加密货币现货/合约,融合在一个板块中可以随意切换,UI非常简洁明了
并且在主页正下方有搜索框可以随意搜索三个板块中的任何新闻/代币/股票等等等
总的来说, @midasmarketsxyz 是真的值得一试,功能很全并且还有积分激励机制(图4)
显示更多


我们对提币作出如下安排:周一 下午4点 BTC、周二 下午4点 ETH、周三 下午4点 USDT、周五 下午4点 全部币种和法币出入金等。
确保在足够安全的环境下让用户有序提币。感谢大家的耐心等待。请见谅因为被盗方式的不同(本次涉及多条非EVM链、10个币种),为了绝对排除所有潜在风险,所以与去年Bybit的处理方式也不一样。
我和Gracy 将在周一下午3点半(提现开始前30分钟)在社区持续直播,就本次安全事件作出讨论,并解答社区提出的问题。
没有天崩地裂,我们将向全世界证明 Bitget 值得信赖🩵
显示更多

重要进展:提现时间将不晚于9月26日04:00(UTC)对外公布,感谢各位用户的耐心等待。
根据最新的链上追踪及交易分类结果,约合3.875亿美元的资产已被转移至多个网络上攻击者控制的地址。
此次数据调整反映的是对事件期间转账情况更完整的核算,新增纳入了此前未计入初步估算范围的 Zcash 及 TRON 链上受影响资产,并不代表出现了新的未经授权转账。该事件持续处于受控状态,不会再发生新的未经授权转账。
此次事件涉及以太坊(Ethereum)及多个 EVM 网络、XRP Ledger、Zcash 及 TRON 上的资产。
截至目前已识别的主要攻击者控制的收款地址如下:
→EVM:0x770b10b273fc44fe9197d6bf20f145c2e98463ee
→XRP:rwNhefsz1UQEusxhCvHip3RANinWi4CTck
→ZEC:t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG
→TRON:TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
已确认受影响的资产包括 XRP、ETH、USDT、ZEC、USDC、USDT0、XAUt、BNB、AVAX 及 TRX。
我们的调查与追踪工作仍在持续进行。上述数据反映的是本文发布时已确认的信息,随着更多交易被分类和追踪,相关数据可能会更新。
该事件持续处于受控状态,自事件得到控制以来未再发生新的未经授权转账,与 Mandiant 及慢雾(SlowMist)的联合调查仍在持续进行。
提现功能仍处于暂时暂停状态,我们正在进行进一步的安全核查与修复工作。
Bitget 将持续通过官方渠道,就调查进展、资产追回、提现恢复以及用户保护基金相关事宜发布经核实的最新信息。
以上内容仅供参考。
显示更多

𝗜𝗠𝗣𝗢𝗥𝗧𝗔𝗡𝗧 𝗨𝗣𝗗𝗔𝗧𝗘𝗦: The withdrawal plan will be announced by September 26th, 4:00 AM UTC. We appreciate your patience on this matter.
Based on the latest onchain tracing and classification of transactions, assets equivalent to approximately $387.5 million were transferred to attacker-controlled addresses across multiple networks.
The revised figure reflects a more complete accounting of transfers that occurred during the incident, adding affected assets on Zcash and TRON that were not included in the initial estimate. It does not reflect further unauthorized transfers.
The incident remains contained and no further unauthorized transfers are possible.
The incident involved assets across Ethereum and several EVM networks, XRP Ledger, Zcash and TRON.
The primary attacker-controlled receiving addresses identified to date are:
→ EVM: 0x770b10b273fc44fe9197d6bf20f145c2e98463ee
→ XRP: rwNhefsz1UQEusxhCvHip3RANinWi4CTck
→ ZEC: t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG
→ TRON: TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
The confirmed affected assets include XRP, ETH, USDT, ZEC, USDC, USDT0, XAUt, BNB, AVAX and TRX.
Our investigation and tracing efforts remain ongoing.
The figures above reflect information confirmed at the time of publication and may be updated as additional transactions are classified and traced.
The incident remains contained, with no further unauthorized transfers since the incident was contained, and the investigation with Mandiant and SlowMist remains ongoing
Withdrawals remain temporarily paused while additional security checks and remediation are underway.
Bitget will continue to provide verified updates on the investigation, asset recovery, withdrawal restoration and the User Protection Fund through its official channels.
𝘍𝘰𝘳 𝘪𝘯𝘧𝘰𝘳𝘮𝘢𝘵𝘪𝘰𝘯𝘢𝘭 𝘱𝘶𝘳𝘱𝘰𝘴𝘦𝘴 𝘰𝘯𝘭𝘺.
显示更多

Bitget 凌晨 3 点被盗约 $3.516 亿资产,其中 EVM 链上被盗约 $1.926 亿 (主要是稳定币跟 ETH)。
EVM 链上被盗的稳定币与其它资产,在过去几小时里被陆续兑换成了 ETH。目前黑客的 EVM 地址持有约 6.85 万枚 ETH ($1.84 亿)。
黑客地址集:
显示更多


🚨 Bitget Hack $350M+ 🚨
满满的恶意,bitget 刚庆祝八周年,又是亚洲凌晨大家睡得最沉的时候...
能观察到的攻击凌晨2点30分就开始了,EVM一侧资金在半个小时之后,接近凌晨3点开始大额转出,攻击的范围包括了Bitget的热钱包和冷钱包,然后一直持续到现在凌晨5点多,足足3个多小时才控制住,哎。
截止黑客已经把大部分EVM资产兑换成 ETH(约6万个)
1️⃣ 疑似冷钱包 (Bitget 35)
0xffa8DB7B38579e6A2D14f9B347a9acE4d044cD54
---
⏰ 凌晨3点16分,第一笔异常交易是的 12,719.46 BNB被盗;紧接着是821,011 AVAX,13,965 ETH;
⏰ 凌晨4点09分,最后一笔1,395 ETH 被转出。
⏰ 凌晨4点40分,疑似安全团队重新控制了这个冷钱包,各种资产开始从其他热钱包地址向这个地址归集。
2️⃣ 主力热钱包 (Bitget 6)
0x1AB4973a48dc892Cd9971ECE8e01DcC7688f8F23
--
⏰ 凌晨2点31分,攻击者发起了一笔小额测试攻击‼️;
⏰ 凌晨2点58分,攻击者发起了大额转出 34.75M USDT,12.85M USDC,7131 ETH;
⏰ 凌晨5点23分,攻击者发起 8.2M AVAX-USDC 转出;
⏰ 凌晨5点23分,攻击者发起 1879 ETH 转出;
⏰ 凌晨5点23分,攻击者发起 233 ETH 转出(最后一笔)
3️⃣ 热钱包 (Bitget 5)
0x5bdf85216ec1e38D6458C870992A69e38e03F7Ef
--
⏰ 凌晨3点01分,3000 XAUT + 5737 OP-ETH
4️⃣ 热钱包 (Bitget 3)
0x97b9D2102A9a65A26E1EE82D59e42d1B73B68689 ⏰ 凌晨3点01分, 1555 Base-ETH
☠️黑客的地址组:
显示更多

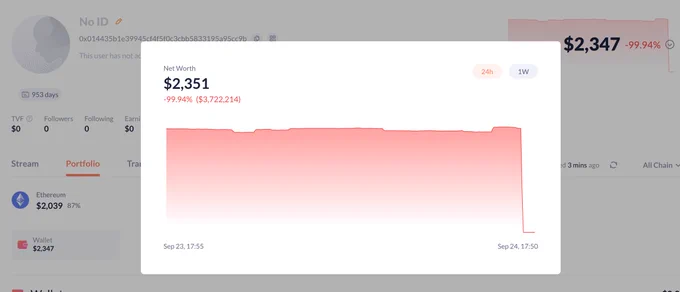
🚨 Duelbits hot wallets on Ethereum, BSC and Tron saw ~$4.2M in outflows to newly created addresses, in a suspected private key compromise.
Assets moved included 836 ETH, 1.62M USDT, 97K USDC, 209 BNB and 192K TRX. Most have since been swapped to ETH.
Duelbits (EVM): 0x014435b1e39945cf4f5f0c3cbb5833195a95cc9b
Duelbits (Tron): THqFmhAPcdHECH3wmrpZv4MWAB2v9TY1oN
Hacker (EVM): 0xa77e24fe29d16e051e487ef4ea7b056cb05aef76
Hacker (Tron): TAvraZZFCZbDSZoyqWWRRsBkFgZqKaCGbK
显示更多


A note on recursive STARK mempools (EIP-8288)
This is an EIP that I am hoping we can get included in I-star (the fork after Hegota) that you can think of as the next step after Frames, that would unlock extreme amounts of power. Particularly:
* Ultra-cheap quantum-safe signatures (SPHINCS-). Much of the cost savings comes from the fact that the signature data (~3 kB) does not have to go onchain
* Ultra-cheap quantum-safe privacy protocols. Status quo minimum cost for private txs is ~300k if you engineer very well (no one does), status quo quantum-safe is ~10M gas, this could reduce it to low tens of thousands.
* Universal support for your favorite new signature or proof scheme without needing EVM changes. Whatever you use (Falcon, ML-DSA, some other lattice-based thing, something code-based or isogeny-based or even more esoteric), you can just wrap it client-side in a STARK, onchain gas cost low tens of thousands just like privacy protocols. Hopefully, Ethereum will never need "please support my favorite cryptographic algo" politics again.
* Private account abstraction: keep your account logic private, and in a private location onchain. Then you can make one transaction to change the ownership of all your onchain state - accounts, defi positions, privacy protocol notes, everything - without revealing which objects' ownership you're changing.
Here's how it works.
Your transaction can include a type of frame that we call a "dependency frame". The frame is a list of statements, asserting claims like "message hash M was signed by SPHINCS- public key P" and "data hash D was proven to satisfy a statement defined by verification key V".
When you send your transaction, you send it in an envelope, which includes a signature or a STARK for each statement in a dependency frame.
Once the transaction reaches the mempool, nodes aggregate them. Each node runs a loop: wait one tick (eg. 500ms), aggregate all new envelopes (either single-tx or multi-tx) that you've seen, remove any transactions that are expired, generate a STARK recursively proving all dependencies, and send a new multi-tx envelope containing that STARK.
Hence, the bandwidth load is bounded: each node's outbound is one STARK (~100-300 kB) per tick, plus each transaction getting broadcasted through the network once (as happens already).
The block builder acts as "yet another mempool node", receiving envelopes from the mempool (plus any side channels), generates its own STARK covering the subset of transactions it intends to include in the block, and adds that STARK to the block.
Total onchain overhead: one STARK (100-300 kB), plus 96 bytes for each statement being proven.
This is what I've called before ( ) "The Proof Singularity". Today, we have all the ingredients to actually implement it.
As a developer, this requires a somewhat different workflow than you are used to, but it is conceptually simple. Any signatures or STARKs, you put into a separate frame. Then the main logic that today is verifying a signature or STARK, you replace with checking for the existence of a frame that includes the correct statement as a dependency.
Examples of useful statements:
* [tx sighash] verifies against [the pubkey at sload(0)]
* there exists a secret and a merkle branch such that hashing secret+0 and applying the merkle branch outputs (public) root R, and hashing secret+1 outputs (public) nullifier N
* there exists a secret address A, salt S and signature Z such that sload(0) = hash(A, S) and a merkle proof of address A inside a recent ethereum state contains some pubkey D where [tx sighash] was signed by D [this is private account abstraction; all variables except [tx sighash] and sload(0) are private; you can also make D a STARK verification key]
* there exists an ML-DSA signature signing [tx sighash], that verifies against an ML-DSA pubkey whose hash is sload(0)
At the core, this is moving any compute and data other than bookkeeping "business logic" outside the core path of Ethereum execution, sharding and parallelizing it via the mempool.
Notice also that this requires agreeing on a _language_ (aka. an ISA) for the recursive STARKs to define statements in. The current leading candidate is RISC-V. So this would also de-facto be Ethereum adding RISC-V (or something else we decide on) as a canonical ISA - a big decision that should be done carefully, but that I think will be necessary to drive Ethereum forward.
显示更多
