与「cignature」相关的搜索结果
cignature 贴吧
一个关键词就是一个贴吧,路径全站唯一。
用户
未找到
包含 cignature 的内容
🆕ドラマ『#私が好きな男X私を好きな男』#
˗ˏˋ📢 #FODプレミアム# で
第1話を独占配信開始❗ ˎˊ˗
💁♀️追う恋愛か追われる恋愛か…🙋♀️
2人の男の間で揺れる女の葛藤を描く💕
第1話「男友達と寝た」
#FOD#
#ゴンチャン#(#B1A4#) #キム・シギョン# #ジウォン#(#cignature#)
▼▼▼
显示更多


HABEMUS TESTNET — DAISUGI v0.1
A post-quantum Ethereum testnet using hash-based SPHINCS signatures with non-native account abstraction.
Big thanks to @riva_labs and @GiulioRebuffo.
Coming next:
• Frame Transactions
• Signature aggregation via LeanSPHINCS
Believe in somETHing. Link ⬇️
显示更多



🚨SlowMist TI Alert🚨
We first reached out to the team privately to responsibly disclose the issue before making any public statement.
💸 @ether_fi Loss: ~15.45 ETH
🔍 Root Cause: `AtomicQueue.solve()` lacks access control on the caller-supplied `solver` — there is no `solver == msg.sender` check, nor any signature, registration, or consent verification. The attacker first created a maliciously crafted `AtomicRequest` using the `updateAtomicRequest()` function, then forced a victim address to act as the `solver`. AtomicQueue subsequently called `finishSolve` on the victim and executed `want.transferFrom(solver, users[i], assetsToUser)`, abusing the victim's pre-existing ERC-20 allowance to drain funds.
📌 Attacker: `0xa5cc6e490bce9185fa47b421f2eac677a83b64ea`
📌 Vulnerable Contract (AtomicQueue): `0xd45884b592e316eb816199615a95c182f75dea07`
Powered by
Tx:
显示更多


A note on recursive STARK mempools (EIP-8288)
This is an EIP that I am hoping we can get included in I-star (the fork after Hegota) that you can think of as the next step after Frames, that would unlock extreme amounts of power. Particularly:
* Ultra-cheap quantum-safe signatures (SPHINCS-). Much of the cost savings comes from the fact that the signature data (~3 kB) does not have to go onchain
* Ultra-cheap quantum-safe privacy protocols. Status quo minimum cost for private txs is ~300k if you engineer very well (no one does), status quo quantum-safe is ~10M gas, this could reduce it to low tens of thousands.
* Universal support for your favorite new signature or proof scheme without needing EVM changes. Whatever you use (Falcon, ML-DSA, some other lattice-based thing, something code-based or isogeny-based or even more esoteric), you can just wrap it client-side in a STARK, onchain gas cost low tens of thousands just like privacy protocols. Hopefully, Ethereum will never need "please support my favorite cryptographic algo" politics again.
* Private account abstraction: keep your account logic private, and in a private location onchain. Then you can make one transaction to change the ownership of all your onchain state - accounts, defi positions, privacy protocol notes, everything - without revealing which objects' ownership you're changing.
Here's how it works.
Your transaction can include a type of frame that we call a "dependency frame". The frame is a list of statements, asserting claims like "message hash M was signed by SPHINCS- public key P" and "data hash D was proven to satisfy a statement defined by verification key V".
When you send your transaction, you send it in an envelope, which includes a signature or a STARK for each statement in a dependency frame.
Once the transaction reaches the mempool, nodes aggregate them. Each node runs a loop: wait one tick (eg. 500ms), aggregate all new envelopes (either single-tx or multi-tx) that you've seen, remove any transactions that are expired, generate a STARK recursively proving all dependencies, and send a new multi-tx envelope containing that STARK.
Hence, the bandwidth load is bounded: each node's outbound is one STARK (~100-300 kB) per tick, plus each transaction getting broadcasted through the network once (as happens already).
The block builder acts as "yet another mempool node", receiving envelopes from the mempool (plus any side channels), generates its own STARK covering the subset of transactions it intends to include in the block, and adds that STARK to the block.
Total onchain overhead: one STARK (100-300 kB), plus 96 bytes for each statement being proven.
This is what I've called before ( ) "The Proof Singularity". Today, we have all the ingredients to actually implement it.
As a developer, this requires a somewhat different workflow than you are used to, but it is conceptually simple. Any signatures or STARKs, you put into a separate frame. Then the main logic that today is verifying a signature or STARK, you replace with checking for the existence of a frame that includes the correct statement as a dependency.
Examples of useful statements:
* [tx sighash] verifies against [the pubkey at sload(0)]
* there exists a secret and a merkle branch such that hashing secret+0 and applying the merkle branch outputs (public) root R, and hashing secret+1 outputs (public) nullifier N
* there exists a secret address A, salt S and signature Z such that sload(0) = hash(A, S) and a merkle proof of address A inside a recent ethereum state contains some pubkey D where [tx sighash] was signed by D [this is private account abstraction; all variables except [tx sighash] and sload(0) are private; you can also make D a STARK verification key]
* there exists an ML-DSA signature signing [tx sighash], that verifies against an ML-DSA pubkey whose hash is sload(0)
At the core, this is moving any compute and data other than bookkeeping "business logic" outside the core path of Ethereum execution, sharding and parallelizing it via the mempool.
Notice also that this requires agreeing on a _language_ (aka. an ISA) for the recursive STARKs to define statements in. The current leading candidate is RISC-V. So this would also de-facto be Ethereum adding RISC-V (or something else we decide on) as a canonical ISA - a big decision that should be done carefully, but that I think will be necessary to drive Ethereum forward.
显示更多


CS 329Z: Engineering AI Agents
Stanford / Fall 2026 @stanfordnlp
课程定位:从"模型"到"系统"的工程学
覆盖:简单 LLM 流水线 → 复合 AI 系统 → 自主 Agent。三位讲师的背景也高度互补:
@Diyi_Yang(斯坦福 NLP 教授,人机交互与社会计算方向)
@michaelryan207(DSPy 核心贡献者,自动评估 AutoMetrics 作者)
@jyangballin(SWE-agent / SWE-bench / SWE-smith 作者,软件工程 Agent 领域最重要的研究者之一)
# 课程主线:三大工程挑战
贯穿全课的三个核心问题——分解(decomposition)、数据(data)、评估(evaluation)。11 周的内容基本围绕这三条线展开,可以分为五个模块:
模块 1:构建基元(Week 2–3)
· LLM 作为构建材料:API/SDK(litellm)、结构化输出、约束生成、解码策略、test-time compute、上下文工程、模型选型与成本/延迟权衡
· RAG:embedding、向量库、分块策略、混合检索、cross-encoder 与 ColBERT 后期交互
· 工具调用:函数调用 API、MCP(Model Context Protocol)、工具设计、代码沙箱、错误处理与重试
模块 2:框架与设计模式(Week 3–5)
· 框架层:DSPy(signature / module / optimizer)、LangChain/LangGraph、LlamaIndex,重点是"框架抽象了什么 vs. 你手写了什么"
· 设计模式:workflow vs. agent 的分类学,五种可组合 workflow 模式,ReAct / plan-and-execute / reflection,"scaffold(脚手架)本身就是设计决策"
· 记忆架构:短期/长期记忆、记忆作为工具动作、文件系统作为外化记忆、跨 Agent 记忆(MemGPT、Mem0、Generative Agents)
· 多 Agent 系统:编排模式、handoff 与状态传递,以及一个很有态度的对照阅读——既读 AutoGen,也读《Why Do Multi-Agent LLM Systems Fail?》和 Neubig 的《Don't Sleep on Single-agent Systems》
模块 3:优化(Week 5)
· 从提示词到微调的全景:GEPA、MIPROv2、OPRO、TextGrad(提示优化);LoRA/QLoRA、蒸馏、RLHF/DPO(权重优化);test-time scaling(推理算力)
· 核心问题是决策框架:什么时候优化 prompt、什么时候优化 weights、什么时候堆推理算力
模块 4:数据与评估(Week 6–8)——最有分量的部分
· 数据:trace、demonstration、feedback 三类数据;训练数据 vs. 评估数据;数据飞轮;合成数据;从 Agent 轨迹构建数据集(SWE-smith)
· 评估基础:为什么 eval 难;4 元组框架(request / environment / stopping criteria / scorer);好 benchmark 的性质;tinyBenchmarks
· 评估基础设施:三类 grader、LLM-as-judge 的 prompt 设计与已知偏差、pairwise vs. pointwise、非确定性指标 pass@k vs. pass^k、harness 设计
模块 5:安全与前沿(Week 8–11)
· 安全:工具访问的隐私风险、prompt injection(含间接注入)、红队、沙箱与权限模型、输出护栏、human-in-the-loop
· Coding Agent:SWE-agent、Claude Code、OpenHands 的端到端架构对比
· 主动式 Agent:从 reactive 到 proactive,General User Models(GUM)、Next Action Prediction,以及"Agent 何时应主动、何时应等待"的 mixed-initiative 问题
· 开放问题:多模态/web/计算机使用 Agent、科学 Agent、长时运行架构、生产可观测性(tracing、monitoring、成本管理)
# 作业设计:一手建、一手评
HW1:从零构建 Agent 系统(10%) 给定论文库,构建能检索并推理回答科学问题的 Agent。
· Part A:只用 litellm 手写 RAG + 工具调用 + ReAct 式 Agent 循环
· Part B:用 DSPy 重建关键组件,并反思框架抽象了什么
HW2:评估一个 Agent(10%) 给定一个预构建 Agent,设计完整评估套件:代码型 grader、至少一个 LLM-as-judge、用 4 元组框架构建 benchmark 任务、错误分析。
显示更多


LATEST: ⚡ Blockstream researchers proposed SHRINCS, a quantum-resistant Bitcoin signature scheme to block attacks that reverse private keys from exposed public keys.


JUST IN: 🏛️🇺🇸 California's "meme coin" bill has passed both the Assembly and Senate.
The legislation prohibits public officers and employees from issuing meme coins and bans listing them for CA residents starting Jan 1, 2027.
AB 2409 now awaits the Governor's signature.
显示更多


LATEST: 🔒 Ethereum devs propose rebuilding the validator deposit contract to allow future quantum-resistant signature types before eventually phasing out today's BLS format, an early step to shield ETH staking from quantum attacks.
显示更多


Welcome Havenex. Series A is underway and closing soon, already applied for all required licenses (even more than required). DM me if interested to invest, note that allocation is already quite packed.
After extensive discussions with regulators, central bank governors, Financial Market Authority leadership, banks, family offices, exchanges, wallet providers and custodians, my mission became very clear:
Build the most transparent, safest, institutional-grade, fully regulated exchange possible, with continuous, verifiable proofs of solvency. Not just web3.
Havenex is not trying to become another Coinbase, Binance, Bybit or Kraken. The focus is different: infra that allows financial institutions to offer digital and traditional financial assets to their customers, while meeting the standards they expect around regulation, custody, security and transparency.
My principles are simple: 100% multi-chain. Verifiable custody. Continuous solvency proofs. Multi-sig by default. Quantum-safe keys. Hardware 2FA wallets. Confidential and RWA assets wherever regulation allows. Unique self-custody and key-loss protection mechanisms.
Some of the best engineers and experts in cryptography, exchanges and privacy-preserving technology are joining the effort.
Havenex will use Sui tech wherever it makes sense, but it will also integrate the best primitives, assets and bridges from other ecosystems.
I'm personally helping Havenex as an advisor, although it was my idea. Mysten Labs and Sui remain my focus, nothing changes there. Chief & Hacker team Officer, as always, innovating at daily basis :)
As all of you know since my Satoshi days, my goal has always been bigger: help crypto meet regulation without sacrificing ownership, transparency or security, while protecting users against malicious and shady activity and giving the best ecosystems room to thrive.
We cannot keep accepting another FTX or Mt. Gox as the cost of doing business, nor the silly, insane bugs driven by LLMs lately. Havenex intends to set a different standard. The most transparent effort in regulatory-friendly crypto. You have my signature.
显示更多
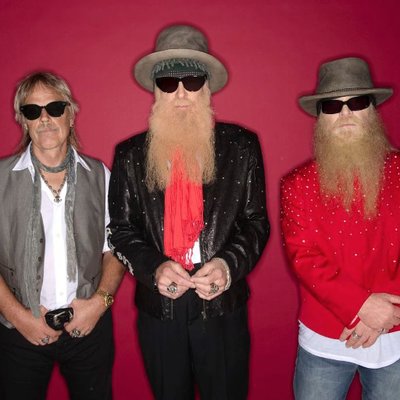
“Today, Elwood and I lost a great friend and collaborator, and the world lost one of the most naturally innovative drummers and a great and true son of Texas. His signature backbeat was key to keeping ZZ on top.” - Billy F Gibbons
显示更多

