SlowMist (@SlowMist_Team) “🚨 SlowMist TI Alert 🚨 MemTensor's AI memory tooling has been compromised: Memo” — TopicDigg


SlowMist
@SlowMist_Team
加入 April 2018
0 正在关注 0 粉丝
🚨 SlowMist TI Alert 🚨
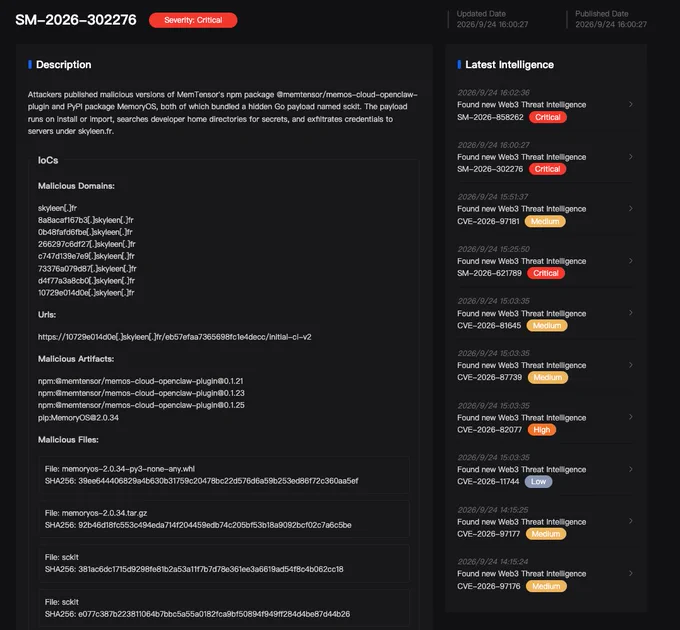
MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's open-source long-term memory library for LLM and AI agents, and memtensor/memos-cloud-openclaw-plugin (npm), the official plugin connecting it to the OpenClaw agent runtime.
Affected versions bundle cross-platform Go binaries that execute when the package is loaded or imported: MemoryOS==2.0.34 on PyPI, and plugin versions 0.1.21, 0.1.23 and 0.1.25 on npm. You are affected if the PyPI version has been imported in your environment, or if the npm plugin is installed and the OpenClaw gateway has been started.
Potential attacker actions include harvesting npm/PyPI tokens, GitHub/GitLab credentials, AWS keys, SSH keys, API tokens, environment secrets, and other developer credentials, with data sent to infrastructure under skyleen[.]fr. The affected npm plugin may also expose user prompt content.
Users should remove or downgrade affected packages to known-good versions (0.1.20 for npm and 2.0.33 for PyPI), terminate sckit processes, block associated infrastructure, review network activity, and rotate credentials accessible from affected environments.
You can also visit to check for free whether the npm packages, pip packages, domains, or IPs you use are safe.
Reference:
As always, stay vigilant!
显示更多