与「SlowMist」相关的搜索结果
SlowMist 贴吧
一个关键词就是一个贴吧,路径全站唯一。
用户
未找到
包含 SlowMist 的内容
MistTrack: Bitget Exploiter Attempted to Route Stolen Funds via Chainflip but Broker Rejected
According to on-chain monitoring by SlowMist's tracking arm MistTrack, the Bitget exploiter attempted to move stolen funds through the cross-chain liquidity protocol Chainflip, but the transaction was rejected at the broker interface ("deposit rejected by the broker"). The protocol did not freeze the capital but instead refunded the deposit directly back to the sender, effectively preventing the attacker from routing the exploit proceeds through the network.
显示更多


On chain investigation made simple by MistTrack Agent powered by @SlowMist_Team available now on @FinchTechCN
Drop a wallet address or tx hash into MistTrack Agent and let it trace fund flows, map connections, and flag potential risks in seconds.
显示更多


继9月24日发现安全事件后,Bitget 将开始分阶段有序恢复提现功能。
此次事件所涉及的漏洞已被查明并完成修复。
Bitget 的安全与技术团队一直在对提现基础设施开展进一步的验证与安全核查,独立网络安全专家 Mandiant 与慢雾(SlowMist)也持续为调查工作提供支持。
提现功能的暂时暂停仍属于安全防范措施,与用户资产的可用性无关。用户账户余额未受任何影响,Bitget 用户保护基金(Protection Fund)将用于覆盖本次平台级事件所造成的资金影响。
安全核查完成后,提现功能将有序恢复。
当前的提现恢复时间安排如下:
9月28日08:00(UTC):BTC(Bitcoin 网络)
9月29日08:00(UTC):ETH(Ethereum、BSC、Arbitrum、Base、Optimism)
9月30日08:00(UTC):USDT(Ethereum、BSC、Solana、Tron)
10月2日08:00(UTC):其他代币/法币/C2C
我们的目标是尽快、安全地恢复所有支持资产及网络的提现服务。
该事件持续处于受控状态,不会再发生新的未经授权转账。在此过程中,用户资金始终不受影响。交易与充值功能持续正常运行。
用户在提现功能逐步开放前无需采取任何操作。提现功能的开放情况将直接在 Bitget 平台上显示,建议用户关注 Bitget 官方渠道以获取最新进展。
显示更多

Bitget will begin resuming withdrawals in orderly phases following the security incident identified on September 24.
The vulnerability involved in the incident has been identified and remediated.
Bitget's security and technical teams have since been conducting additional validation and security checks across the withdrawal infrastructure, while independent cybersecurity experts Mandiant and SlowMist continue to support the investigation.
The temporary withdrawal pause remains a security measure and is not related to the availability of user assets. User account balances remain unaffected, and Bitget's Protection Fund covers the financial impact of this platform-wide incident.
Withdrawals will resume in an orderly manner once these security checks are completed.
The current withdrawal resumption schedule is as follows:
> Sep 28, 8:00 (UTC): BTC (Bitcoin Network)
> Sep 29, 8:00 (UTC): ETH (Ethereum, BSC, Arbitrum, Base, Optimism)
> Sep 30, 8:00 (UTC): USDT (Ethereum, BSC, Solana, Tron)
> Oct 2, 8:00 (UTC): Other Tokens / Fiat / P2P
Our objective is to restore withdrawal services across all supported assets and networks as quickly and safely as possible.
The incident remains contained, and no further unauthorized transfers are possible. User funds are unaffected throughout this process. Trading and deposits continue to operate.
Users do not need to take any action ahead of the rollout. Withdrawal availability will be reflected directly on the Bitget platform, and users are advised to follow Bitget's official channels for updates.
显示更多
重要进展:提现时间将不晚于9月26日04:00(UTC)对外公布,感谢各位用户的耐心等待。
根据最新的链上追踪及交易分类结果,约合3.875亿美元的资产已被转移至多个网络上攻击者控制的地址。
此次数据调整反映的是对事件期间转账情况更完整的核算,新增纳入了此前未计入初步估算范围的 Zcash 及 TRON 链上受影响资产,并不代表出现了新的未经授权转账。该事件持续处于受控状态,不会再发生新的未经授权转账。
此次事件涉及以太坊(Ethereum)及多个 EVM 网络、XRP Ledger、Zcash 及 TRON 上的资产。
截至目前已识别的主要攻击者控制的收款地址如下:
→EVM:0x770b10b273fc44fe9197d6bf20f145c2e98463ee
→XRP:rwNhefsz1UQEusxhCvHip3RANinWi4CTck
→ZEC:t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG
→TRON:TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
已确认受影响的资产包括 XRP、ETH、USDT、ZEC、USDC、USDT0、XAUt、BNB、AVAX 及 TRX。
我们的调查与追踪工作仍在持续进行。上述数据反映的是本文发布时已确认的信息,随着更多交易被分类和追踪,相关数据可能会更新。
该事件持续处于受控状态,自事件得到控制以来未再发生新的未经授权转账,与 Mandiant 及慢雾(SlowMist)的联合调查仍在持续进行。
提现功能仍处于暂时暂停状态,我们正在进行进一步的安全核查与修复工作。
Bitget 将持续通过官方渠道,就调查进展、资产追回、提现恢复以及用户保护基金相关事宜发布经核实的最新信息。
以上内容仅供参考。
显示更多

重要更新!#提币时间将于明天中午12点前公布。感谢您的耐心等待。# 关于今天安全事件的最新进展,详情如下:
1、安全团队已精准定位本次黑客攻击路径与攻击手法,并掌握攻击者绕过安全防护的相关细节,距离溯源攻击源头已十分接近。第三方安全团队 Mandiant 和 SlowMist 的事故调查仍在进行中,详细报告等待安全团队出具。
2、链上追踪已确认,共计约3.875亿美元被转移至黑客地址(此前预估3.516亿),此次修正包含了 $ZEC 和 $TRX 目前未发现其他未经授权的转移。本次针对平台层面被盗资金将全由Bitget用户保护基金覆盖,用户资产不受任何损失。
3、现正式启动资金恢复赏金计划:自愿主动冻结攻击者资金可获得 5% 的赏金,自愿主动追回资金可获得 5% 的赏金。赏金同样适用于已提供的帮助。Bitget 公布了攻击者地址、实时追踪仪表盘和提交门户,大家也可以通过Bybit 的 Lazarusbounty 平台提交。交易所、安全研究人员和链上调查人员——我们需要你们的帮助 🙏
实时资金追踪仪表盘:
提交资金恢复或冻结信息:
攻击者地址 API — 实时更新的高级追踪器:
显示更多
𝗜𝗠𝗣𝗢𝗥𝗧𝗔𝗡𝗧 𝗨𝗣𝗗𝗔𝗧𝗘𝗦: The withdrawal plan will be announced by September 26th, 4:00 AM UTC. We appreciate your patience on this matter.
Based on the latest onchain tracing and classification of transactions, assets equivalent to approximately $387.5 million were transferred to attacker-controlled addresses across multiple networks.
The revised figure reflects a more complete accounting of transfers that occurred during the incident, adding affected assets on Zcash and TRON that were not included in the initial estimate. It does not reflect further unauthorized transfers.
The incident remains contained and no further unauthorized transfers are possible.
The incident involved assets across Ethereum and several EVM networks, XRP Ledger, Zcash and TRON.
The primary attacker-controlled receiving addresses identified to date are:
→ EVM: 0x770b10b273fc44fe9197d6bf20f145c2e98463ee
→ XRP: rwNhefsz1UQEusxhCvHip3RANinWi4CTck
→ ZEC: t1WgMdtND8NF7NDUuYmq8MpMj1NTCXkMDVG
→ TRON: TBWNguTTgezw9dVorX441C6nDrZpRxYwKD
The confirmed affected assets include XRP, ETH, USDT, ZEC, USDC, USDT0, XAUt, BNB, AVAX and TRX.
Our investigation and tracing efforts remain ongoing.
The figures above reflect information confirmed at the time of publication and may be updated as additional transactions are classified and traced.
The incident remains contained, with no further unauthorized transfers since the incident was contained, and the investigation with Mandiant and SlowMist remains ongoing
Withdrawals remain temporarily paused while additional security checks and remediation are underway.
Bitget will continue to provide verified updates on the investigation, asset recovery, withdrawal restoration and the User Protection Fund through its official channels.
𝘍𝘰𝘳 𝘪𝘯𝘧𝘰𝘳𝘮𝘢𝘵𝘪𝘰𝘯𝘢𝘭 𝘱𝘶𝘳𝘱𝘰𝘴𝘦𝘴 𝘰𝘯𝘭𝘺.
显示更多
有很多小伙伴希望我问问 @Bitget_zh 提币开放的事情,我确实和小伙伴们沟通了一下,之前 Bybit 被盗后快速开放提币是因为只有 ethereum:native 单币被盗,所以管控相对会简单一些,而且当时也是非常快定位到是多签渠道产生的问题。
而这次 Bitget 的被盗涉及多个币种、多条网络,所以会复杂更多一些。这个情况下交易所出于对安全的考虑都不敢贸然开提币。最起码想要找到还有没有其它的漏洞,避免提币以后再出问题。
如果我个人分析是正确的话,这次被盗的损失也就是不到一年的利润,不至于让 Bitget 出大问题的。另外目前 Bitget 也请了第三方专家 Mandiant 和 SlowMist 合作调查。
当然也希望能早日找到漏洞,尽快开启提币,安抚小伙伴的情绪。
显示更多
[UPDATES] We are currently working with independent third-party experts Mandiant and SlowMist for a full investigation.
Our first priority is our users. User balances remain intact, and Bitget's User Protection Fund covers the impact on this platform-wide incident.
Bitget Wallet operates as a self-custodial wallet on a completely separate and independent infrastructure from Bitget Exchange and was not affected by this incident.
Bitget Wallet users' assets remain onchain under users' control and remain unaffected.
The Bitget Exchange platform continues to operate normally.
Withdrawals are still temporarily paused while we complete additional security checks, and we will restore them as soon as we are confident that it is safe to do so.
We know that during an incident like this, users want answers quickly. We will provide timely updates through Bitget's official channels.
显示更多

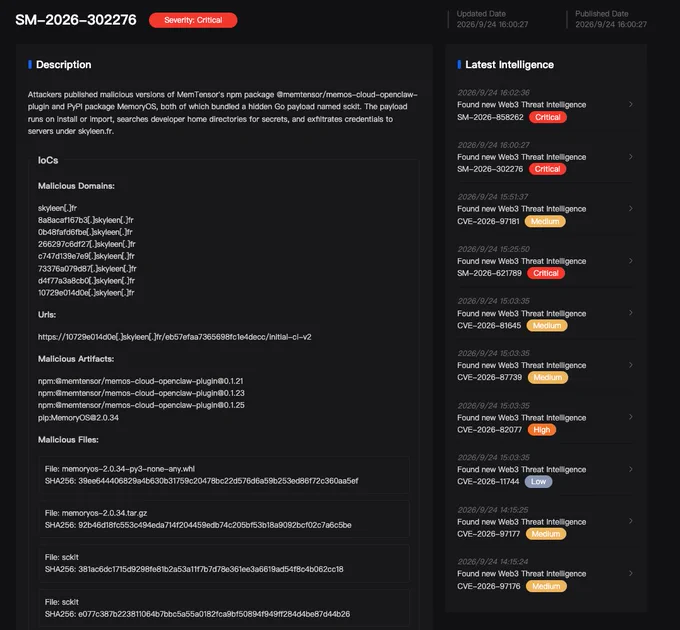
🚨 SlowMist TI Alert 🚨
MemTensor's AI memory tooling has been compromised: MemoryOS (PyPI), the company's open-source long-term memory library for LLM and AI agents, and memtensor/memos-cloud-openclaw-plugin (npm), the official plugin connecting it to the OpenClaw agent runtime.
Affected versions bundle cross-platform Go binaries that execute when the package is loaded or imported: MemoryOS==2.0.34 on PyPI, and plugin versions 0.1.21, 0.1.23 and 0.1.25 on npm. You are affected if the PyPI version has been imported in your environment, or if the npm plugin is installed and the OpenClaw gateway has been started.
Potential attacker actions include harvesting npm/PyPI tokens, GitHub/GitLab credentials, AWS keys, SSH keys, API tokens, environment secrets, and other developer credentials, with data sent to infrastructure under skyleen[.]fr. The affected npm plugin may also expose user prompt content.
Users should remove or downgrade affected packages to known-good versions (0.1.20 for npm and 2.0.33 for PyPI), terminate sckit processes, block associated infrastructure, review network activity, and rotate credentials accessible from affected environments.
You can also visit to check for free whether the npm packages, pip packages, domains, or IPs you use are safe.
Reference:
As always, stay vigilant!
显示更多