

Cos(余弦)😶🌫️ (@evilcos)
@evilcos
0 正在关注 0 粉丝
强如 Telegram 创始人的人,对网络安全的理解也并不高明。果然术业专攻。AI 再强也改变不了人类自建的信息茧房。
Re alleged RCE in new TG Android/Windows widgets:
The issue doesn’t exist.
No one could be hacked just by receiving a message.
You had to start a 3rd party service first.
Even that is fully patched server-side.
Think otherwise? Go hack my account: 🍿
显示更多


We’ve published an update on our recent security incident. See a detailed overview of what happened and our remediation steps here:


🚨 SlowMist TI Alert 🚨
After receiving user reports of stolen funds, we looked into @PennysiaLabs. The Settlement contract on Ethereum was exploited through an arbitrary external call, which let the attacker spend users’ leftover token approvals. 🔧
⚠️ Anyone who ever approved tokens to the Settlement contract should revoke now 👇
0x3aad97e5a91b8e43b7dc830aceb004307678795e
Attacker: 0x813a5ab666adeba907548235fbac087642878300
Attack tx:
显示更多


对于大多数人来说,基础安全都一堆问题,还需要什么高级利用?高级利用更是降维打击。
AI 加速一切,可惜人的惰性和傲慢是永恒的。
@407875776 同样,永远不要把助记词保存在备忘录里,哪怕你备忘录加了个密码。
1/ 🛡️ Compliance can’t pause.
SlowMist offers free trials and dedicated technical support to help businesses maintain their on-chain risk screening and compliance workflows, while exploring alternative or complementary #KYT# solutions. 👇 🧵
显示更多
一些主流钱包(包括硬件钱包、iOS/安卓/浏览器扩展钱包等)我其实都放了至少 1 ETH 价值资金,有的可能更多些,比如我公开的这个地址 wowcos.eth 等。如果这些钱包真的出了大问题,我肯定也会是受害者。以身入局,整整齐齐👀
还逐步给某些 Agent 类钱包也分配了点资金,看看有没有惊喜…
显示更多
@salmanmunir96 @ChangeNOW @HashDit Please ignore this contract and transaction. It’s unrelated to your stolen funds — it’s a common fake ERC-20 log event scam.
新版 Telegram 支持消息里带“应用”,但没有沙盒保护,使用的 QuickJS 有可能成为恶意代码触发执行…真感觉 Telegram 脑抽了,花里胡哨容易引入不必要的风险,现在的 AI 漏洞挖掘和利用已经远胜从前。
建议等等,暂不更新 Telegram。
显示更多

Telegram shipped a "sandbox" for HTML widgets in messages. It's an in-process QuickJS (C) interpreter on a thread...
No fork, no isolatedProcess, no seccomp anywhere in the tree, so any QuickJS exploit is enough to gain full control with whatever privileges the Telegram client is running as without the need for any separate sandbox escape
The bug is a UaF in the interpreter, from standard JS:
```js
class D { [Symbol.dispose]() {} }
const d = new D();
let leak;
class C { static {
for (await using x of [d, d]) leak = () => x;
}}
// ... run anything ...
leak() // reads a freed frame
```
The fix for this particular vuln is still just in the master branch, and considering the number of vulnerabilities QuickJS has had in the past, this vuln will surely not be the last...
显示更多
虽然…但是,原来 Ledger 的 Clear Signing 机制默认会采集 Ledger 用户签名时的网络/链 ID、目标地址(合约或收款人)、设备型号、固件版本、应用版本、是否盲签及原因等。
这个隐私采集机制不在 Ledger 固件里,在 Ledger SDK(context-module v1.16+),所以需要支持 Ledger 连接的钱包应用来提供开关。
显示更多

This is part of how Clear Signing works. ERC-7730 descriptors, which turn raw calldata into readable fields, are too large to fit on a Ledger signer, and most integrators don’t want to bundle the full metadata set.
So the default context module in our signing kit resolves them from Ledger’s servers at signing time. That requires sending the transaction details needed to find the right descriptor. Ledger doesn’t store that data.
It runs in the developer library that wallet apps use to talk to a Ledger signer, not in device firmware.
Integrators control it and can supply their own context module to resolve metadata themselves:
How the context module works:
The descriptor registry is public:
显示更多


继续友情提醒下:iOS 又有安全更新了…iPhone 已经不如以往那样的“安全”,各种恶意利用在冒出…
不乱安装 App,不乱打开陌生网页(尤其涉黄的…
以前这种提醒主要都是针对 Windows 的,时代变了🤣
显示更多
把 SlowMist Agent Security Skill 扔给 DeepSeek Harness,用“创造模式”:
参考 编写一个适合 DSH 的安全插件。
然后按你对安全的理解,对话几轮,一个适配该 Agent 的安全插件就出来了。
显示更多


🚨 ClickFix has a new trick... the malicious payload is already sitting in your browser cache before you paste the command.
Compromised sites preload scripts disguised as PNGs, letting pasted commands bypass Windows Run's ~260-character limit and launch a multi-stage malware chain.
Read:
显示更多

🚨SlowMist TI Alert🚨
💸 @SetProtocol Loss: ~5.08 ETH
🔍 Root Cause: actualizeFee() recalculated unitShares with upward rounding even though no fee was minted, raising it from 4,927 to 4,928. The attacker issued before the update and redeemed the same quantity afterward, extracting collateral from the rounding-induced unit increase. Uniswap v4 flash accounting supplied temporary liquidity to scale the exploit.
📌 Attacker (EOA): 0x506440728d84eb22809dc9464bc8189618a1c5b6
📌 Attack Contract: 0x016feaaa25ab8325e233bc8a2c25055bee0b2f6e
📌 Victim (Set Protocol Vault): 0x5b67871c3a857de81a1ca0f9f7945e5670d986dc
📌 Vulnerable Contract: 0x54e8371c1ec43e58fb53d4ef4ed463c17ba8a6be
Powered by
Tx:
显示更多

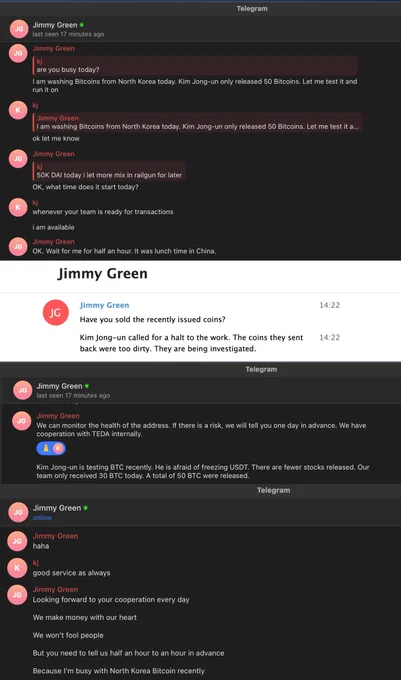
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
显示更多

🚨SlowMist TI Alert🚨
💸 MALT Loss: ~$72k
🔍 Root Cause: swap(uint256,uint256,address) records the caller’s input and pre-swap reserves, then invokes an external rebalanceHook before transferring the requested output. The hook withdraws DAI from the Capital Source and deposits it into the same pool. The swap subsequently validates its invariant against the pool’s final balances, treating this protocol-funded DAI as if it were supplied by the caller. Because the function does not isolate caller-funded input from hook-funded rebalancing capital, an attacker can provide negligible input, trigger treasury-funded liquidity injection, and withdraw a disproportionate amount of MALT.
📌 Attacker: 0x8F103B6A0aD705bcE6357842A5fefEB49e8D83Ef
📌 Victim: 0xF0d314849A3Bc9270a79110F25dBA2c8325A2AAC
📌 Vulnerable Contract: 0xfe6C096a2871337d4f6F7DD04Ebda733E94D7A13
Powered by
Tx:
显示更多
🚨SlowMist TI Alert🚨
💸 @Goldpesatoken Loss: ~$114.9k
🔍 Root Cause: GPXHooks' reBalance() performs liquidity operations through the shared, flash-accounted PositionManager inside an attacker-controlled PoolManager unlock without verifying that the PositionManager's GPX/USDC currency deltas are zero, so the hook's burn credit is not isolated from the caller's state. The attacker opens an unlock, mints a WETH/USDC position via MINT_POSITION without settling (leaving the shared PositionManager with a −114,999.999187 USDC delta), then swaps on the GPX pool to trigger the hourly rebalance: the hook burns its real position and earns a +148,868.602189 USDC credit, but TAKE_PAIR can only withdraw the net positive delta, so the hook receives just 33,868.603002 USDC while the attacker's phantom debt absorbs the difference. Burning its own position cancels that debt and the attacker takes 114,999.999186 USDC straight out of the PoolManager — a missing delta-isolation / zero-delta check on a shared PositionManager.
📌 Attacker: 0x4a5FD2e9357cC87DF4cD6A1808174DBc8646899F
📌 Victim: 0x4519e2b040ff1B64fa03aBe2AeF0BC99D7CcEaA8
📌 Vulnerable Contract: 0x4519e2b040ff1B64fa03aBe2AeF0BC99D7CcEaA8
Powered by
Tx:
显示更多











